Public APIs, Agents & MCP
Workbench2 is the operator control plane. It exposes two HTTP APIs, two kinds of credentials, an in-app Ecosystem Agent, and a Workbench MCP server. Those surfaces are not the Java Runtime scoring APIs (POST /invocations then POST /response).
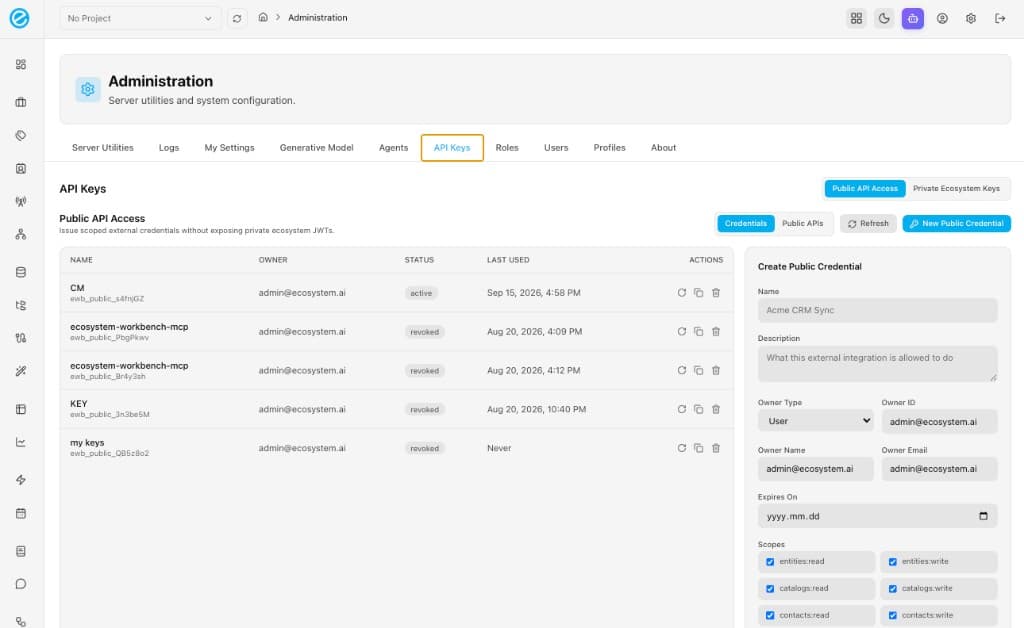
Open Administration → API Keys (admin role). Switch Public API Access and Private Ecosystem Keys. Agents is the neighbouring tab.
Surfaces at a glance
| Surface | Default local URL | Who uses it | Auth |
|---|---|---|---|
| Private Workbench API | http://localhost:8001/api/v1 | Workbench SPA, Campaign Management, internal services | Workbench session JWT (Authorization: Bearer) |
| Public API gateway | http://localhost:8004/public/v1 | Notebooks, partners, MCP harness, external apps | Dual: X-API-Key: ewb_public_… and a user JWT |
| Workbench MCP | POST http://localhost:8001/mcp | Ecosystem Agent, Cursor, Claude Code | In-process for /assistant; dual-auth for HTTP MCP |
| LLM proxy | POST http://localhost:8001/v1/messages | Agent SDK / Claude Code | Workbench JWT; no Anthropic key in the image |
| Runtime scoring | http://localhost:8091/invocations | Production apps, Runtime Dashboard | Runtime config; closed loop uses /response (singular) |
| Runtime MCP | POST http://localhost:8091/mcp | Agents that score campaigns | Separate from Workbench MCP |
./backend/run.sh starts the private API on 8001 and the public gateway on 8004. The Vite UI on 5270 talks to :8001 and does not proxy /mcp.
Which credential?
Public credentials (ewb_public_…) never replace private ecosystem JWTs. Issue scoped public keys for integrations. Keep private keys for Grafana, ecosystem-server, and other platform services that expect a generated ecosystem JWT.
| Credential | Tab | Prefix / shape | Purpose |
|---|---|---|---|
| Public API Access | Public API Access | ewb_public_… | Scoped gateway + HTTP MCP. Shown once on create/rotate. |
| Private Ecosystem Keys | Private Ecosystem Keys | Server-generated JWT | Grafana, ecosystem-server, platform services. Stored in ecosystem_meta.api_keys. |
Create public credentials with an owner (user, service account, organization, or partner), optional expiry, and scopes. The Public APIs sub-tab shows which routes the selected scopes unlock.
Typical access paths
- Browser operator — sign in to Workbench. The SPA uses the private API with your session JWT. No public key.
- External integration — mint a public credential, obtain a user JWT (
POST /public/v1/auth/loginor Workbench login), call:8004/public/v1/…with both headers. - Ecosystem Agent — Administration → Agents or
/assistant. In-process MCP; no public key. - Cursor / Claude Code — dual-auth
POST /mcpplusANTHROPIC_BASE_URLpointing at Workbench:8001forPOST /v1/messages. - Campaign scoring — Runtime
POST /invocationsthenPOST /response. Workbench MCPscore_customer/send_feedbackwrap a deployment; they are not RuntimePOST /mcp.
Pages in this section
- API Keys — issue, rotate, revoke
- Public APIs — gateway routes and scopes
- Private APIs —
:8001/api/v1routers - Agents — product catalog and Ecosystem Agent
- MCP — Workbench vs Runtime vs sidecar
Related: API Management (test Runtime scoring from Workbench), Runtime API Access, Runtime MCP.